Buy maschinenvermietung.eu ?
We are moving the project
maschinenvermietung.eu .
Are you interested in purchasing the domain
maschinenvermietung.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy maschinenvermietung.eu ?
Is SQL injection still possible in 2019?
Yes, SQL injection is still possible in 2019. Despite advancements in security measures and awareness about this vulnerability, many websites and applications are still vulnerable to SQL injection attacks. It remains a common attack vector for hackers to exploit and gain unauthorized access to databases. It is crucial for developers to implement proper input validation and parameterized queries to prevent SQL injection attacks. **
Is an SQL injection attempt punishable by law?
Yes, an SQL injection attempt can be punishable by law. In many jurisdictions, attempting to exploit vulnerabilities in computer systems, including SQL injection attacks, can be considered a criminal offense under laws related to unauthorized access to computer systems, data theft, or computer fraud. Penalties for such offenses can include fines, imprisonment, or other legal consequences. It is important for individuals to understand and comply with the laws and regulations related to computer security and data protection to avoid legal repercussions. **

Similar search terms for SQL injection
Top-Angebote
Products related to SQL injection:
-
DELPHI HRP711 Injection pumpTecDoc Engine Number: 31846, 35247, 28614, 28616, 28615, 29483, 33420, 30806, 29484, 35605, 35606, 35607, 30546, 35608, 35609, 37509, 37510, 30548, 30560, 30550, 30563, 30557, 31019, 31080, 31064, 31020, 31087, 31088, 31089, 31090, 31092, 31091, 31097, 31094, 31096, 31095, 31098, 31099, 39484, 35050, 33435, 33763, 32331, 32332, 33434, 33263, 28617, 33003, 33002, 33704, 33708, 39140, 39489, 33770, 31484, 35296, 35205, 35257, 35342, 39737, 35497, 36094, 35984, 36861, 38279, 48023, 38280, 39048, 39049, 39051, 39050, 39047, 39052, 48026, 46332, 39155, 39156, 40859, 40860, 41881, 41880, 41882, 41883, 47426, 47425, 49000, 45677; Engine Code: DW10FD, DW10FC, DW10FE, DW12RUE, DW12RUD; Construction Year from: 05/2014, 01/2010, 01/2014, 10/2014, 12/2014; for model code: Fap, K0; Emissions Standard: Euro 6478,99 £*Shipping: 1,99 £Secure redirect to the provider


-
How can one prevent SQL injection and Cross-Site Scripting?
To prevent SQL injection, one can use parameterized queries or prepared statements in their code to ensure that user input is treated as data rather than executable code. Additionally, input validation can be implemented to restrict the type and format of user input. To prevent Cross-Site Scripting, one can sanitize user input by encoding special characters and validating input fields to only allow certain types of data. Using security mechanisms like Content Security Policy (CSP) can also help prevent XSS attacks by restricting the sources from which resources can be loaded on a webpage. Regularly updating software and libraries, as well as conducting security audits, can also help prevent both SQL injection and Cross-Site Scripting vulnerabilities. **
-
Can you give me exercises on the topic of SQL injection?
Sure! Here are a few exercises you can try to practice SQL injection: 1. Use a vulnerable web application or a purposely built SQL injection lab to practice exploiting SQL injection vulnerabilities. Try to manipulate the input fields to inject SQL commands and retrieve sensitive information from the database. 2. Write your own simple web application with a vulnerable input field and try to exploit it using SQL injection. This will help you understand how SQL injection works and how to prevent it in your own code. 3. Research and practice using different types of SQL injection techniques, such as error-based, union-based, and blind SQL injection. This will give you a better understanding of the various ways attackers can exploit SQL injection vulnerabilities. Remember to always practice ethical hacking and only test on systems that you have permission to access. **
-
How can one rewrite SQL questions into SQL commands?
To rewrite SQL questions into SQL commands, one can start by identifying the specific data that needs to be retrieved or manipulated. Then, the question can be translated into SQL commands such as SELECT, INSERT, UPDATE, or DELETE, depending on the specific task at hand. It's important to ensure that the SQL commands are structured correctly and include the necessary clauses such as WHERE, GROUP BY, or ORDER BY to achieve the desired outcome. Additionally, one should consider any necessary joins or subqueries to retrieve data from multiple tables. **
-
What is better: direct injection or intake manifold injection?
Direct injection is generally considered better than intake manifold injection because it allows for more precise fuel delivery, resulting in improved fuel efficiency and power output. Direct injection also reduces the risk of carbon buildup on the intake valves, which can be a common issue with intake manifold injection. Additionally, direct injection allows for better control over the air-fuel mixture, leading to cleaner emissions. Overall, direct injection is the preferred choice for modern engines due to its superior performance and efficiency. **
What is SQL and what does an SQL server do?
SQL, or Structured Query Language, is a programming language used to manage and manipulate data in relational databases. It allows users to create, retrieve, update, and delete data from databases, as well as define and manipulate the structure of the data. An SQL server is a software application that is used to store and manage databases, allowing multiple users to access and manipulate the data concurrently. It provides a secure and efficient way to store and retrieve data, and can handle large volumes of data and complex queries. **
How does the fat-dissolving injection or injection lipolysis work?
The fat-dissolving injection, also known as injection lipolysis, works by injecting a solution directly into the targeted area of fat. This solution contains a synthetic form of deoxycholic acid, which is a naturally occurring substance in the body that helps break down and absorb dietary fat. Once injected, the solution breaks down the fat cells, causing them to rupture and be eliminated by the body's natural processes. Over time, the treated area will appear slimmer and more contoured as the fat cells are gradually removed. **
Top-Angebote
Products related to SQL injection:
-
Microsoft SQL Server 2019 Standard (CAL) - Full licenceMicrosoft SQL Server 2019 Standard (CAL) - Full licence Microsoft SQL Server 2019 Standard (CAL) is the ideal solution for companies and professionals looking for a powerful, secure and highly scalable database. This edition offers all the fundamental functionalities to reliably manage, store and analyse data, guaranteeing high performance and business continuity. Thanks to the licence model Server + CAL (Client Access Licence) , you can easily manage user or device access, while maintaining full control over costs and security. Main features High performance: Intelligent query optimisation and better support for complex workloads. Maximum security: Advanced features such as Always Encrypted, Data Classification and auditing to protect your data. Enhanced integration: Compatible with business intelligence, data analysis and machine learning tools. High availability: Support for failover and replication clusters to minimise downtime. Flexible scalability: Ideal for SMEs and growing companies that need a stable, high-performance infrastructure. What the licence includes Licence SQL Server 2019 Standard Model Server + CAL Suitable for Windows Server environments Immediate activation and dedicated technical support For whom it is ideal Companies in need of a secure and high-performance database platform IT professionals and developers Organisations requiring precise access control via CALs ERP solutions, CRM, management and mission-critical applications87,99 £*Shipping: 0,00 £Secure redirect to the provider
-
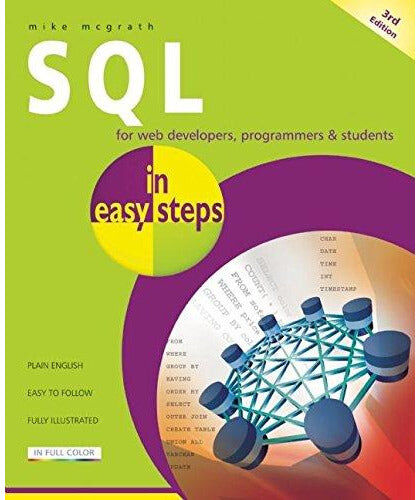
In Easy Steps Limited SQL In Easy Steps 3rd EditionSQL in easy steps, 3rd edition has an easy-to-follow style that will appeal to anyone who wants to begin using databases. It is aimed at those with little or no experience of SQL. From web developers wanting to add database interaction to their web sites, programmers wanting to quickly add SQL to their skills set, hobbyists who want to begin creating SQL scripts for upload to their own ISP, to students or to those seeking a career in computing, this book will appeal to all who need a fundamental understanding of database administration with SQL. SQL in easy steps, 3rd edition begins by explaining how to download and install the free MySQL database server on both Windows and Linux platforms. This allows you to establish an environment in which to develop and administer your own databases. This book makes no assumption that you will have previous knowledge of any programming or scripting language so it's ideal for the newcomer to SQL. Each chapter builds your knowledge of executing database queries. The book contains exciting chapters on how to selectively extract data from within one, or more, databases and there are complete examples that illustrate each aspect of SQL. By the end of this book you will have gained a sound understanding of the Structured Query Language and be able to write your own SQL scripts to insert, extract and manipulate data. Updated and revised with the latest techniques since the second edition, which was published in 2005. All examples given in this 3rd edition demonstrate SQL features using the MySQL Relational Database Management System that is supported on both Windows and Linux operating systems. Table of Contents Introducing SQL Getting Started Creating database tables Inserting data into tables Retrieving data from tables Sorting retrieved data Simple data filtering Complex data filtering Generating calculated fields Manipulating data Grouping table data Making complex queries Joining database tables5,49 £*Shipping: 2,99 £Secure redirect to the provider
-
DELPHI HRP711 Injection pumpTecDoc Engine Number: 31846, 35247, 28614, 28616, 28615, 29483, 33420, 30806, 29484, 35605, 35606, 35607, 30546, 35608, 35609, 37509, 37510, 30548, 30560, 30550, 30563, 30557, 31019, 31080, 31064, 31020, 31087, 31088, 31089, 31090, 31092, 31091, 31097, 31094, 31096, 31095, 31098, 31099, 39484, 35050, 33435, 33763, 32331, 32332, 33434, 33263, 28617, 33003, 33002, 33704, 33708, 39140, 39489, 33770, 31484, 35296, 35205, 35257, 35342, 39737, 35497, 36094, 35984, 36861, 38279, 48023, 38280, 39048, 39049, 39051, 39050, 39047, 39052, 48026, 46332, 39155, 39156, 40859, 40860, 41881, 41880, 41882, 41883, 47426, 47425, 49000, 45677; Engine Code: DW10FD, DW10FC, DW10FE, DW12RUE, DW12RUD; Construction Year from: 05/2014, 01/2010, 01/2014, 10/2014, 12/2014; for model code: Fap, K0; Emissions Standard: Euro 6478,99 £*Shipping: 1,99 £Secure redirect to the provider
-
Is SQL injection still possible in 2019?
Yes, SQL injection is still possible in 2019. Despite advancements in security measures and awareness about this vulnerability, many websites and applications are still vulnerable to SQL injection attacks. It remains a common attack vector for hackers to exploit and gain unauthorized access to databases. It is crucial for developers to implement proper input validation and parameterized queries to prevent SQL injection attacks. **
-
Is an SQL injection attempt punishable by law?
Yes, an SQL injection attempt can be punishable by law. In many jurisdictions, attempting to exploit vulnerabilities in computer systems, including SQL injection attacks, can be considered a criminal offense under laws related to unauthorized access to computer systems, data theft, or computer fraud. Penalties for such offenses can include fines, imprisonment, or other legal consequences. It is important for individuals to understand and comply with the laws and regulations related to computer security and data protection to avoid legal repercussions. **
-
How can one prevent SQL injection and Cross-Site Scripting?
To prevent SQL injection, one can use parameterized queries or prepared statements in their code to ensure that user input is treated as data rather than executable code. Additionally, input validation can be implemented to restrict the type and format of user input. To prevent Cross-Site Scripting, one can sanitize user input by encoding special characters and validating input fields to only allow certain types of data. Using security mechanisms like Content Security Policy (CSP) can also help prevent XSS attacks by restricting the sources from which resources can be loaded on a webpage. Regularly updating software and libraries, as well as conducting security audits, can also help prevent both SQL injection and Cross-Site Scripting vulnerabilities. **
-
Can you give me exercises on the topic of SQL injection?
Sure! Here are a few exercises you can try to practice SQL injection: 1. Use a vulnerable web application or a purposely built SQL injection lab to practice exploiting SQL injection vulnerabilities. Try to manipulate the input fields to inject SQL commands and retrieve sensitive information from the database. 2. Write your own simple web application with a vulnerable input field and try to exploit it using SQL injection. This will help you understand how SQL injection works and how to prevent it in your own code. 3. Research and practice using different types of SQL injection techniques, such as error-based, union-based, and blind SQL injection. This will give you a better understanding of the various ways attackers can exploit SQL injection vulnerabilities. Remember to always practice ethical hacking and only test on systems that you have permission to access. **
Similar search terms for SQL injection
-
How can one rewrite SQL questions into SQL commands?
To rewrite SQL questions into SQL commands, one can start by identifying the specific data that needs to be retrieved or manipulated. Then, the question can be translated into SQL commands such as SELECT, INSERT, UPDATE, or DELETE, depending on the specific task at hand. It's important to ensure that the SQL commands are structured correctly and include the necessary clauses such as WHERE, GROUP BY, or ORDER BY to achieve the desired outcome. Additionally, one should consider any necessary joins or subqueries to retrieve data from multiple tables. **
-
What is better: direct injection or intake manifold injection?
Direct injection is generally considered better than intake manifold injection because it allows for more precise fuel delivery, resulting in improved fuel efficiency and power output. Direct injection also reduces the risk of carbon buildup on the intake valves, which can be a common issue with intake manifold injection. Additionally, direct injection allows for better control over the air-fuel mixture, leading to cleaner emissions. Overall, direct injection is the preferred choice for modern engines due to its superior performance and efficiency. **
-
What is SQL and what does an SQL server do?
SQL, or Structured Query Language, is a programming language used to manage and manipulate data in relational databases. It allows users to create, retrieve, update, and delete data from databases, as well as define and manipulate the structure of the data. An SQL server is a software application that is used to store and manage databases, allowing multiple users to access and manipulate the data concurrently. It provides a secure and efficient way to store and retrieve data, and can handle large volumes of data and complex queries. **
-
How does the fat-dissolving injection or injection lipolysis work?
The fat-dissolving injection, also known as injection lipolysis, works by injecting a solution directly into the targeted area of fat. This solution contains a synthetic form of deoxycholic acid, which is a naturally occurring substance in the body that helps break down and absorb dietary fat. Once injected, the solution breaks down the fat cells, causing them to rupture and be eliminated by the body's natural processes. Over time, the treated area will appear slimmer and more contoured as the fat cells are gradually removed. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.